Certificate-based access for every researcher and device
Every user and device proves its identity with its own credentials or certificate, with no passwords to share or steal.
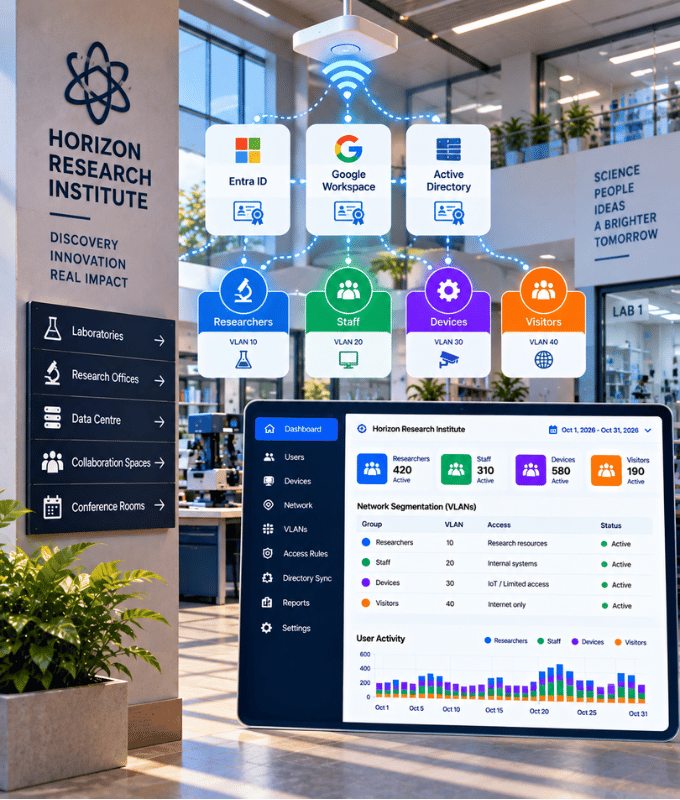
Keep each group on its own VLAN, with access that changes as soon as your directory does.
How we help research institutes
Wi-Fi that verifies every connection, and shows you who is on your network.
Certificate-Based Access
With EAP-TLS, devices authenticate with digital certificates instead of passwords, which we can issue and renew for you.
Individual Credentials
Every user and device connects with their own credentials or certificate, instead of one shared password.
Zero Trust
Every user and device is verified, and gets only the access its role needs, on its own network segment.
Separate Networks for Separate Groups
Place groups on different VLANs, based on their directory groups, to keep traffic apart.
Multi-Factor Authentication
Require a second verification factor on top of the password for stronger protection of network access.
Always in Sync
Changes in your directory apply on the network automatically: new users get access, and disabled users lose it.
Know Who Connected
Keep detailed authentication and session logs, so you always know who connected, when and from where.
Professional Services
Our network experts can help with design, predictive surveys, installation, testing and more, for new sites or upgrades to your existing network.
Solutions for Research Institutes
The Splash Networks solutions and services that fit your venue best.
Identity & Access Management
Network access driven by Active Directory, Entra ID or Google Workspace.
Frequently Asked Questions
How do researchers connect to the Wi-Fi?
With 802.1X, each user or device signs in with their own credentials or certificate, checked against your user directory, instead of a shared password.
Do you support certificate-based authentication?
Yes. With EAP-TLS, devices authenticate with digital certificates instead of passwords, which gives the strongest, phishing-resistant security.
Do you support a zero trust approach?
Yes. Every user and device is verified with its own identity, gets only the access its role needs, and is kept on its own network segment. Access is re-evaluated as identities change, and every connection is logged.
Which user directories can it connect to?
SQL databases, Google Workspace, LDAP, Active Directory and Microsoft Entra ID, among others. If your directory isn't listed, get in touch: we can integrate with other identity sources too.
Do you support multi-factor authentication?
Yes. You can require a second verification factor on top of the password for stronger protection of network access.
Will it work with our existing Wi-Fi equipment?
Splash Networks works with access points and routers from many vendors. See our Supported Hardware page, or ask us about your equipment.
Have more questions? Ask your question here
Companies all over the world are using our products and services