RADIUS authentication for ISPs, WISPs and enterprises
Cloud or on-premises RADIUS, set up and configured by our network engineers.
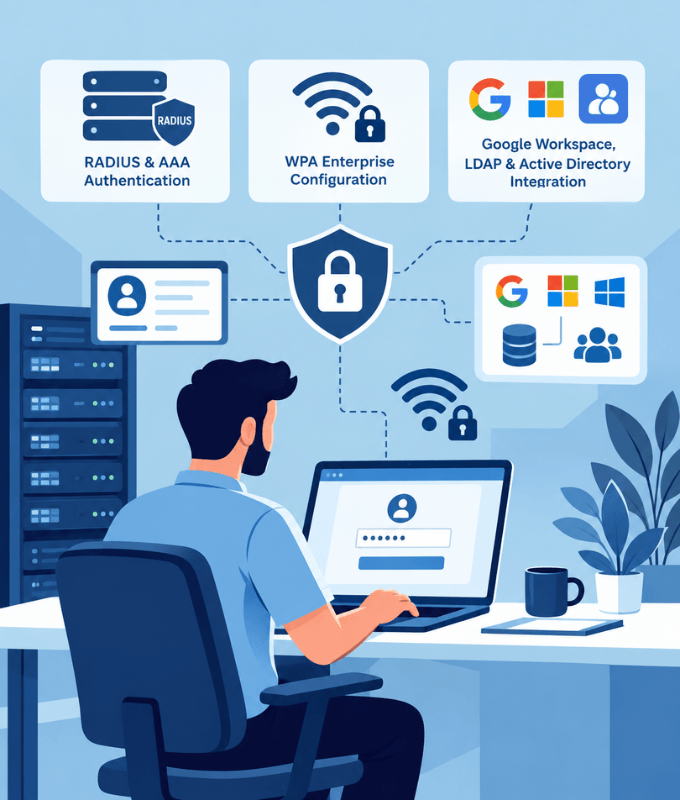
Authenticate users against the directories you already use, including SQL, Google Workspace, LDAP, Active Directory and Microsoft Entra ID.
From 802.1X, EAP and certificate-based authentication with MFA, to quotas, billing and dynamic policies with CoA.
Cloud or on-premises RADIUS
Run RADIUS wherever it suits your network best.
Cloud RADIUS
RADIUS in the cloud, with no server hardware at your sites. A good fit for networks spread across many locations.
On-Premises RADIUS
RADIUS on your own servers, so authentication and user data stay inside your network.
Authentication, authorization and accounting for every use case
Centralized Authentication
One place to authenticate users and devices across all your sites, access points and network equipment.
Authorization
Control what each user or device can access after they connect, from one central server.
Accounting & Billing
Track sessions and usage to bill subscribers, from ISP plans to paid Wi-Fi access.
Policy Management
Define access policies for users, groups and devices, and apply them consistently across your network.
Dynamic Policies with CoA
Change a live session's policy or disconnect a user instantly with Change of Authorization (CoA), with no reconnect needed.
Bandwidth & IP Assignment
Set upload and download speed limits, and assign IP addresses or address pools, per user, group or plan.
Time & Volume Quotas
Limit access by time online or data used, for example to enforce subscriber plans or fair use.
Logging & Reporting
Keep detailed authentication and session logs, and report on users, sessions and usage.
Certificate-Based Authentication
Authenticate devices with digital certificates instead of passwords, for stronger, phishing-resistant security.
Multi-Factor Authentication
Require a second verification factor on top of the password for stronger protection of network access.
802.1X / WPA-Enterprise
Give every user their own credentials on your network, instead of one shared password.
Passpoint (Hotspot 2.0)
Let devices join your Wi-Fi automatically and securely, with no captive portal or manual sign-in.
Flexible EAP support
The most common 802.1X methods, and others when you need them. Choose what fits your users, devices and security requirements.
EAP-TLS
Certificate-based authentication on both the client and the server. The strongest option, with no passwords to steal.
PEAP
Username and password sent inside an encrypted TLS tunnel. Widely supported and easy to roll out.
EAP-TTLS
Username and password inside a TLS tunnel, with flexible inner authentication methods for different directories.
Other EAP Methods
Need something else? We can work with other EAP methods your devices or network require.
SQL Databases
Google Workspace
LDAP
Active Directory
Microsoft Entra ID
And More
Connect the user directories you already use
Authenticate users against your existing identity source, so there's no separate user database to maintain.
Integrations with SQL databases, Google Workspace, LDAP, Active Directory, Microsoft Entra ID and other identity providers.
Let users sign in to WPA-Enterprise Wi-Fi with their Google Workspace accounts. See how with FreeRADIUS and Secure LDAP
Assign VLANs and policies based on directory groups. See how with Google Workspace Secure LDAP
Don't see your directory? We can integrate with other identity sources too. Talk to us
RADIUS for every kind of network
We build and integrate RADIUS for service providers and enterprises alike.
ISPs
Subscriber authentication, accounting and billing for internet service providers.
WISPs
Authenticate and manage subscribers across your wireless towers and hotspots.
Enterprises
Secure, centralized network access for staff, guests and devices, connected to your corporate directory.
Companies all over the world are using our products and services
Frequently Asked Questions
Common questions about our RADIUS and AAA services.
What is RADIUS (AAA)?
RADIUS is the standard protocol networks use for Authentication (who is connecting), Authorization (what they can access) and Accounting (what they used). Access points, switches and other network equipment send login requests to a RADIUS server, which checks them against your user directory.
Should I choose cloud or on-premises RADIUS?
Cloud RADIUS suits networks spread across many locations and avoids running server hardware. On-premises RADIUS keeps authentication and user data inside your own network. We'll help you choose based on your requirements.
Which user directories can RADIUS connect to?
SQL databases, Google Workspace, LDAP, Active Directory and Microsoft Entra ID, among others. If your directory isn't listed, get in touch: we can integrate with other identity sources too.
Do you support 802.1X and certificate-based authentication?
Yes. We support 802.1X (WPA-Enterprise), including certificate-based authentication, so users and devices connect with their own credentials instead of a shared password.
What is Change of Authorization (CoA)?
CoA lets the RADIUS server update an active session, for example to change a user's policy or disconnect them, without the user having to reconnect. It's what makes dynamic policies possible.
Who do you provide RADIUS services for?
ISPs, WISPs and enterprises, with use cases ranging from subscriber billing to centralized authentication, policy management and Passpoint.
Which EAP methods do you support?
We support EAP-TLS for certificate-based authentication, plus PEAP and EAP-TTLS for username and password logins inside an encrypted tunnel. We can also work with other EAP methods your devices or network require, and we'll help you pick the right one.
Can I limit users' time, data or speed?
Yes. RADIUS can enforce time and volume quotas, set bandwidth limits and assign IP addresses per user, group or plan, and CoA lets you change these on live sessions.