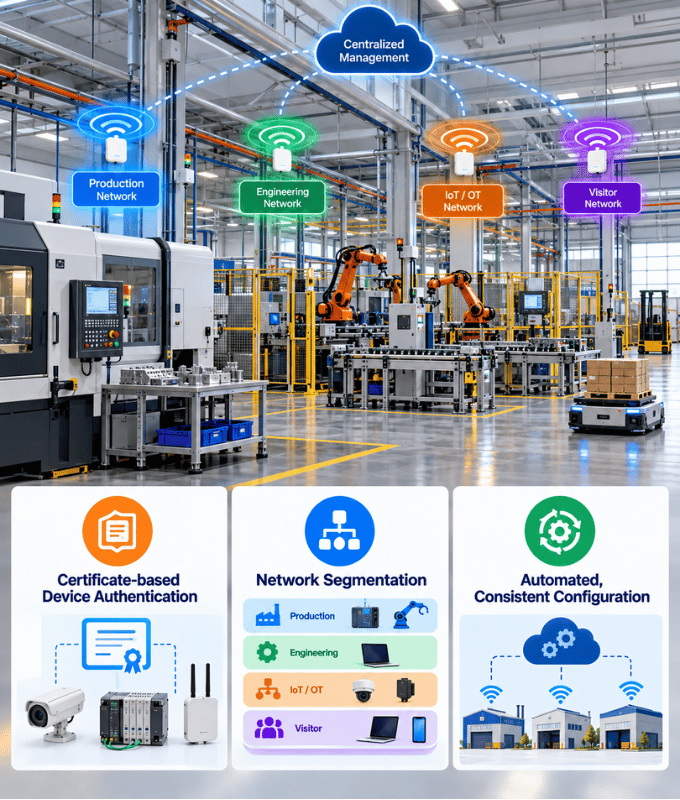
Certificates for your devices, separate networks for every group
Devices authenticate with certificates instead of passwords, and each group stays on its own network.
Automate the repetitive configuration, so every site and device is set up the same way.
How we help manufacturing and industrial sites
Wi-Fi that verifies every device, keeps groups apart and is configured the same way everywhere.
Certificate-Based Access
With EAP-TLS, devices authenticate with digital certificates instead of passwords, for the strongest, phishing-resistant security.
Separate Networks for Separate Groups
Place groups on different VLANs, based on their directory groups, to keep traffic apart.
Zero Trust
Every user and device is verified, and gets only the access its role needs, on its own network segment.
Devices Kept Separate
Devices such as smart TVs, printers and IoT devices get their own unique Wi-Fi password with xPSK, separate from staff and visitors.
Lock Accounts to Devices
Lock an account to specific devices by MAC address, so credentials can't be used on other devices.
Network Automation
Automate repetitive configuration, provisioning and changes, so they're done the same way every time.
Know Who Connected
Keep detailed authentication and session logs, so you always know who connected, when and from where.
Professional Services
Our network experts can help with design, predictive surveys, installation, testing and more, for new sites or upgrades to your existing network.
Solutions for Manufacturing & Industrial Sites
The Splash Networks solutions and services that fit your venue best.
Network Development
Network automation, integrations between systems and custom network software.
Frequently Asked Questions
How do staff connect to the Wi-Fi?
With 802.1X, each staff member signs in with their own credentials or certificate, checked against your user directory, instead of a shared password.
Do you support certificate-based authentication?
Yes. With EAP-TLS, devices authenticate with digital certificates instead of passwords, which gives the strongest, phishing-resistant security.
Do you support a zero trust approach?
Yes. Every user and device is verified with its own identity, gets only the access its role needs, and is kept on its own network segment. Access is re-evaluated as identities change, and every connection is logged.
Can different groups be kept on separate networks?
Yes. Users can be placed on different VLANs and given different policies, such as rate limits, based on their directory groups.
How do devices that can't use 802.1X connect?
Devices such as smart TVs, printers and IoT devices can use xPSK instead, with a unique password for each device. Many networks combine 802.1X for staff with xPSK for devices and a captive portal for guests.
Will it work with our existing Wi-Fi equipment?
Splash Networks works with access points and routers from many vendors. See our Supported Hardware page, or ask us about your equipment.
Have more questions? Ask your question here
Companies all over the world are using our products and services